README
This README is the one indexed from the repository at its latest ref, not from the tag for this version.
Noir is a SAST tool that reads source code and extracts the endpoints an application exposes — paths, methods, parameters, headers, cookies, and the source files behind them. Shadow APIs, deprecated routes, and undocumented handlers come out as part of the same inventory; they aren't a separate mode.
The inventory feeds three audiences:
- Human reviewers. Security engineers and code auditors get a focused list of attacker-reachable entrypoints — paths, parameters, source files, tags — instead of skimming the whole repo.
- AI auditors. LLM-based SAST agents get the same focused list, plus per-endpoint review context (
--include calleefor 1-hop callees,--ai-contextfor guards, sinks, validators, and signals). - DAST tools. ZAP, Burp Suite, Caido and Gori get a real route list to scan, including paths they would never have reached by crawling.
What Noir does
- Endpoint extraction. Static analysis across 205 frameworks. Returns endpoints, parameters, headers, cookies, and the source files they came from.
- LLM fallback. Hand unsupported frameworks (or one-off custom routing) to OpenAI / Ollama / etc. when static rules don't apply.
- Output for the next stage. JSON, YAML, OpenAPI, SARIF, cURL, Postman, HTML — whichever format the next tool in the pipeline reads.
- DAST integration. Pipe directly into ZAP, Burp Suite, Caido or Gori as a proxy target, or export OpenAPI for them to import.
- AI SAST context. The endpoint inventory (and, with
--include callee, the 1-hop functions each handler invokes) is the focused context an LLM auditor needs to find attacker-reachable bugs.--ai-contextgoes further and attaches aggregated review context per endpoint — guards, callees, sinks, validators, and signals — so the LLM doesn't have to rediscover them. - CI/CD. GitHub Action, SARIF output, exit codes — fits the pipeline you already have.
Usage
noir -hExample
noir -b <source_dir>If you use it with Github Action, please refer to this document .
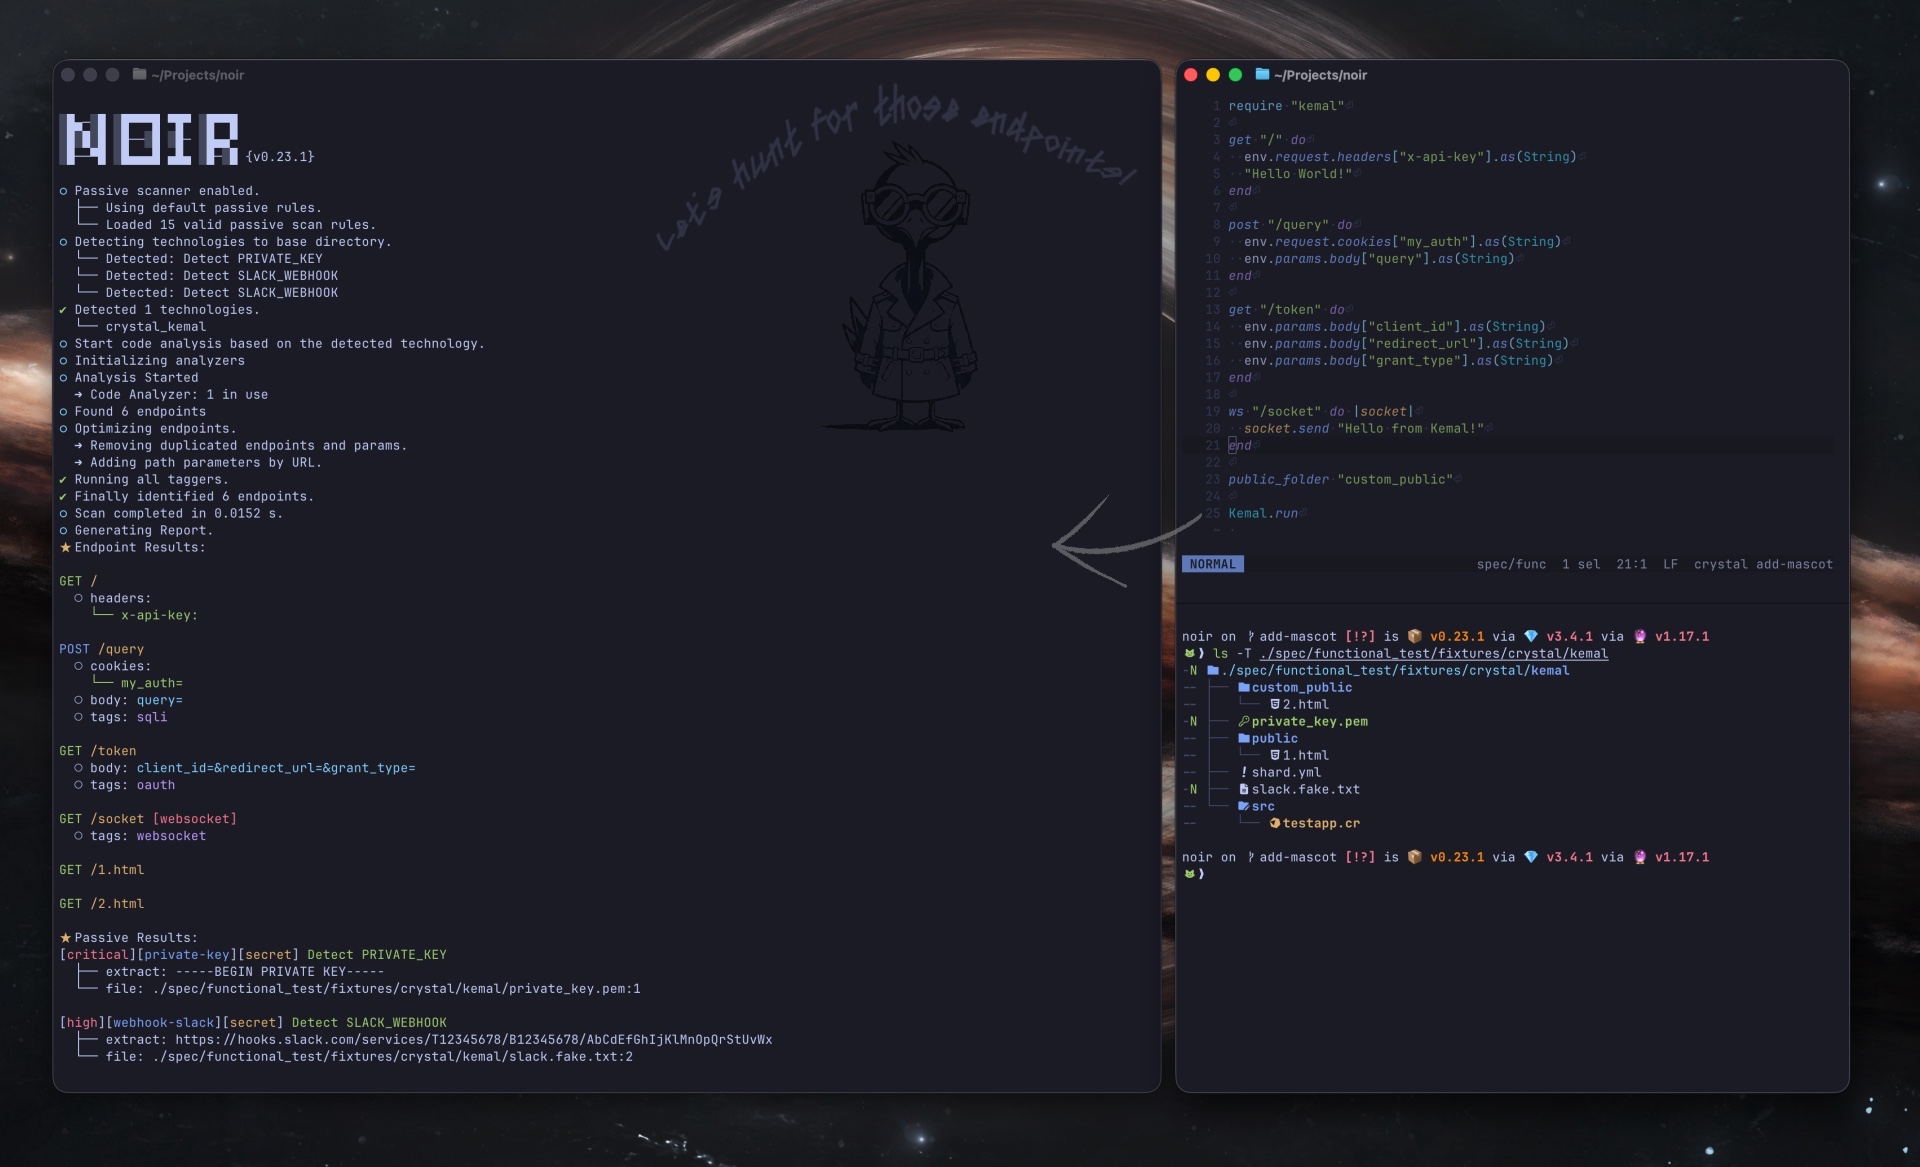
For more details, please visit our documentation page.
Roadmap
Noir started as a WhiteBox testing aid: extract endpoints from source so DAST can scan them more accurately. The job has grown — the same inventory now feeds human auditors and AI SAST agents too. The goal from here is to serve all three consumers equally well: humans reviewing the code, LLMs auditing it, and DAST tools scanning it.
From here:
- Broaden language and framework coverage; keep accuracy honest with per-framework fixtures.
- Lean harder on LLMs for the cases static analysis can't reach.
- Enrich the per-endpoint review context (guards, callees, sinks, validators, signals) so human reviewers and AI auditors share the same focused view of each handler.
- Keep DAST integration first-class — OpenAPI, proxy targets, and direct hand-offs to ZAP / Burp / Caido.
OWASP Project
OWASP Noir joined the OWASP Foundation in June 2024.
- Official project page: https://owasp.org/www-project-noir/
- OWASP Nest: https://nest.owasp.org/projects/noir
News & Updates
- May 2026: Released v1.0.0 — introducing a stable 1.x line across all analyzers, taggers, passive-scan, and a brand new verb-centric CLI structure.
- May 2026: Refreshed the roadmap — Noir's goal is now to serve humans, AI auditors, and DAST tools equally as consumers of the same endpoint inventory.
- August 2025: Presented at the OWASP Seoul Meetup. (Open Source Gardening)
- November 2024: Published a guest blog post "Powering Up DAST with ZAP and Noir" on the ZAP blog.
- June 2024: Joined OWASP as OWASP Noir
- Renamed the GitHub organization from noir-cr to owasp-noir
- Transitioned to co-leadership with @ksg97031
- November 2023: Moved the Noir repository to the noir-cr GitHub organization.
- August 2023: Started as @hahwul's personal project.
Core Team
Contributing
Noir is an open-source project made with ❤️. If you would like to contribute, please check CONTRIBUTING.md and submit a Pull Request.
Mascot
 | Our mascot is Hak (학), a crane symbolizing elegance and precision in spotting hidden flaws. In Korean, "학" means "crane," representing a sharp ally who dives deep to uncover vulnerabilities and attack surfaces in your code. For more artwork and resources related to Hak, check out noir-artwork repository. |
|---|